Security and trust
Patient data stays with the right hospital, branch and person
Isolation, access control and audit are built into every layer of Docran, and tested on every change.
Branch isolation, enforced twice
The application filters every record by hospital and branch, and the database itself refuses to return another branch's rows.
Fails closed
A missing setting blocks the action and says what to configure. Actions stay disabled until the permission is confirmed.
Complete audit trail
Sign-ins, role changes and configuration edits are written to an append-only log in the same step as the change.
No patient data in logs
Logs and telemetry carry identifiers only. Nothing about a patient stays in the browser after logout or a branch switch.
Password or SMS sign-in
Staff sign in with a password or a one-time SMS code. Session tokens rotate, and reuse of an old token is detected.
Scanned on every change
Each release is checked for leaked secrets, patient-shaped data and vulnerable container images before it can deploy.
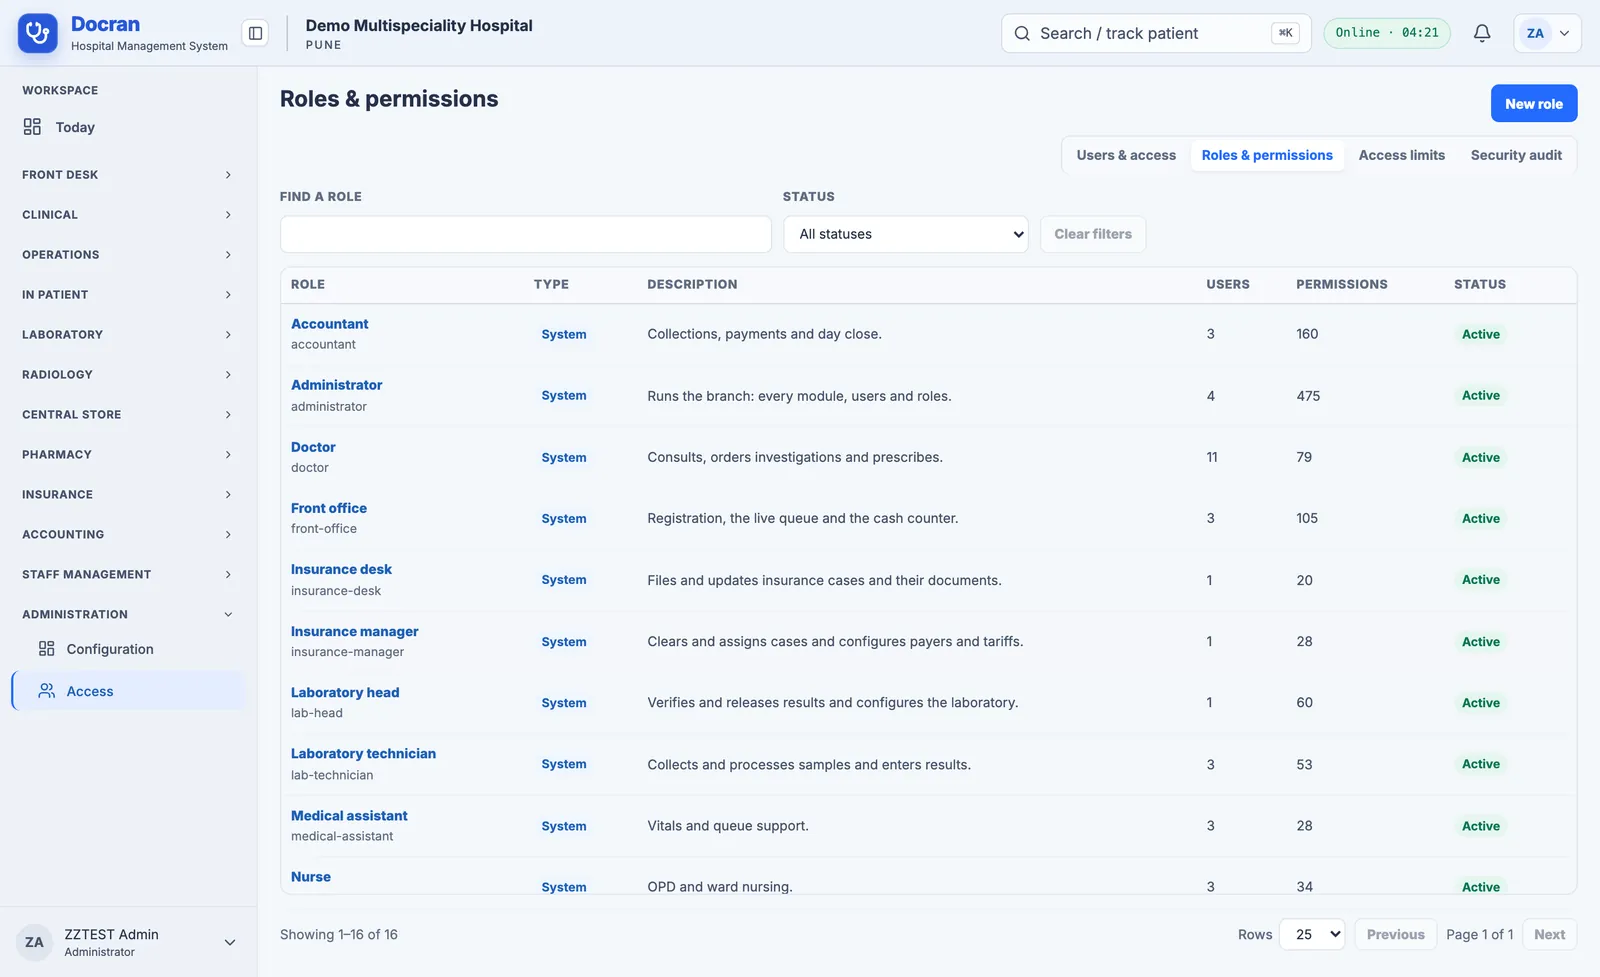
Access built from permissions
Sixteen ready-made roles, more than 450 permissions, and per-person limits. Every endpoint is gated, and a test fails the build if one is not.
- Roles are bundles of permissions you can edit
- Limits can only remove access
- Security audit screen for administrators
Hosted in India
Docran runs on Google Cloud in the Mumbai region, with database migrations applied before each release and images deployed by exact version.
- Google Cloud, asia-south1 (Mumbai)
- PostgreSQL 17 with row-level security
- Releases verified before they go live