Trust Centre
What Indian hospitals ask before they sign, answered plainly
Where the data lives, who can see it, and what Docran is aligned with.
India's DPDP Act, 2023
Patient data, protected by law.
Encrypted in transit and at rest. Shown only to the role that needs it. Every access and every change written to an audit trail the hospital can read.
The Indian checklist
Digital Personal Data Protection Act 2023
Consent recorded at registration, access limited by role and purpose, no patient data in logs or browsers, data in India, a Data Processing Addendum with every hospital.
Data residency
Hosted in the cloud in an Indian region; backups and processing stay in India.
Branch and hospital isolation
Every row carries the hospital and branch; the application filters by both and the database refuses other branches' rows on its own.
Audit trail
Sign-ins, role changes, configuration edits and money corrections written to an append-only log in the same transaction as the change.
NABH documentation
Consent management, record release with audit, medication chart with witness sign-off, discharge from intent to final bill.
ABDM and ABHA
Aligned with the Ayushman Bharat Digital Mission framework for ABHA linking and health-record exchange.
ISO 27001 and SOC 2
Aligned with ISO 27001 and the SOC 2 Trust Services Criteria for information-security controls.
GST and HSN
HSN codes and GST on pharmacy bills; GST on purchase orders.
IST everywhere
Every displayed date and time is Indian Standard Time; day boundaries at IST midnight.
Service levels
Availability and support commitments are set out in each hospital's agreement.
Security inside the product
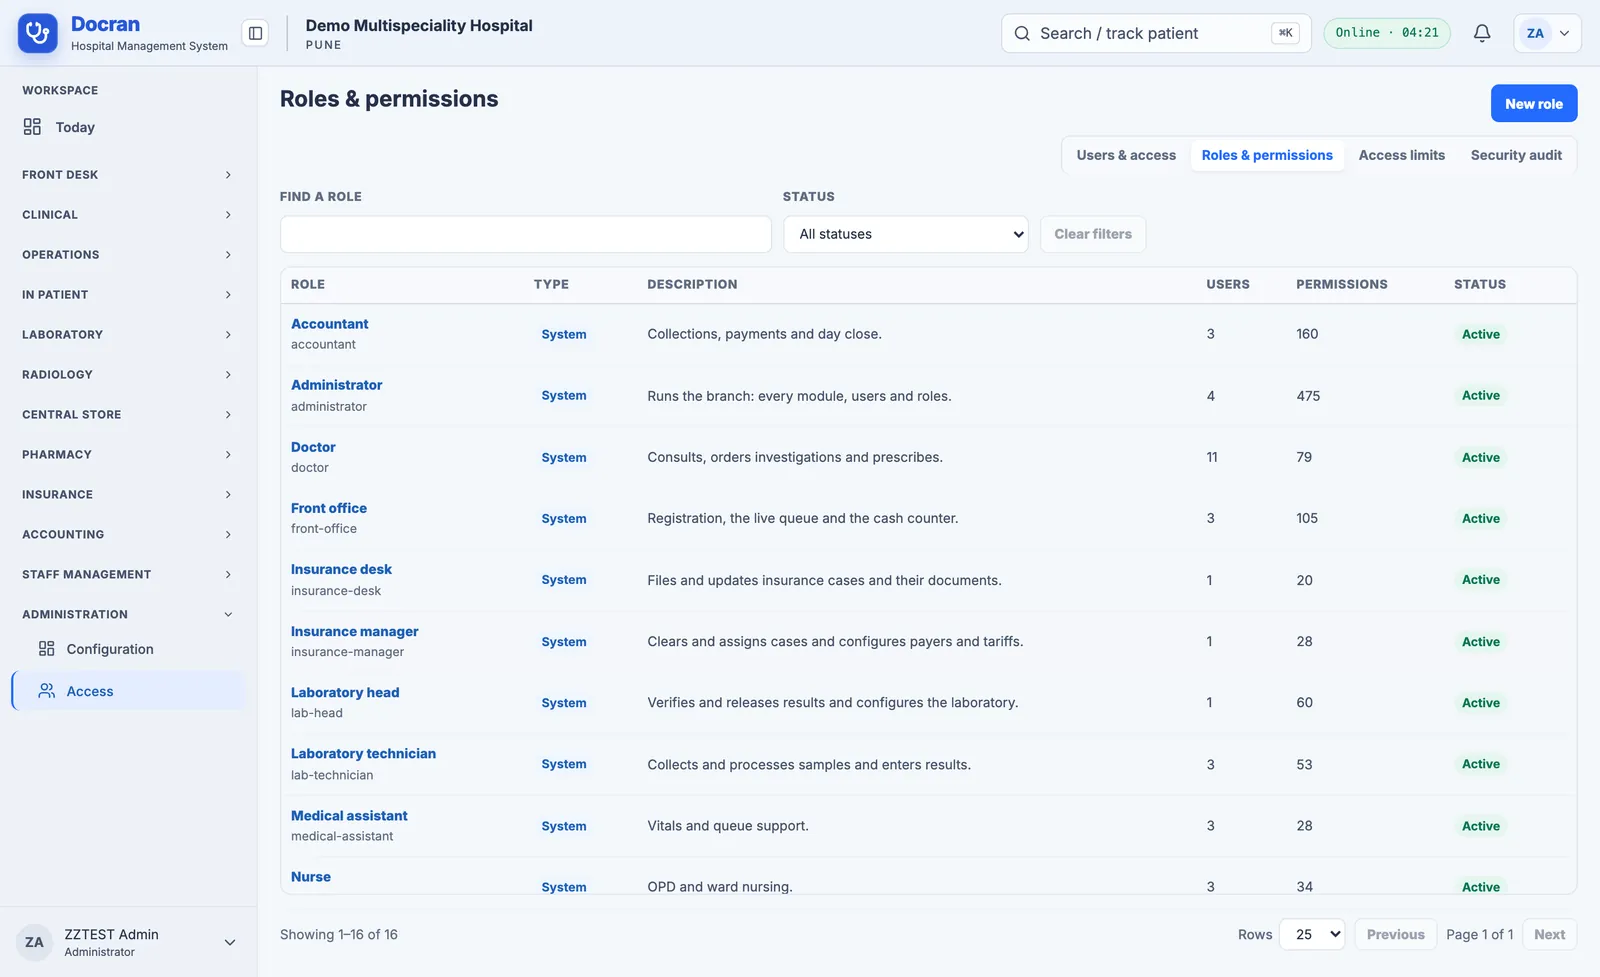
Sixteen roles and 475 permissions gate every screen and endpoint; a test fails the build if one is left open. Session tokens rotate, and reuse of an old token ends the session.
- Per-person limits can remove access, never add it
- Hidden values say "Hidden for your role"
- Maker and checker on refunds, dues and payments
How a release reaches a hospital
More than 5,000 automated tests, a secret scan and an image scan before every release; database changes applied first; every image deployed by exact version.
- Synthetic patients only in development and test
- No real patient data leaves a hospital's database
- A written release record for every deployment
Release Deployment record
Sub-processors
- Cloud hosting in an Indian region
- SMS and email providers for sign-in codes and notices
- The named list in every hospital's Data Processing Addendum
Documents on request
- Data Processing Addendum (DPDP Act 2023)
- Security questionnaire and architecture summary
- Release and change-control description
Responsible disclosure
- Report to security@docran.in
- Acknowledged within 48 hours
- No action against good-faith research that respects patient data